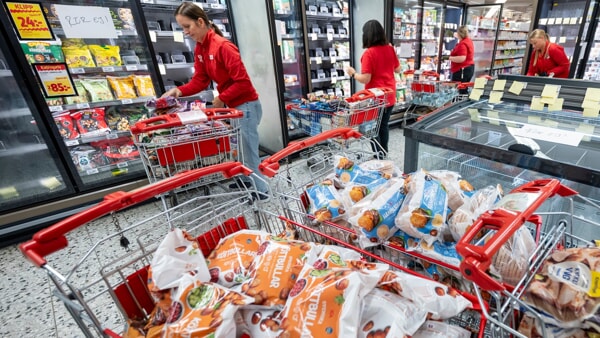
Behind him hacker attacks to hundreds of supermarkets across half of Europe, Including Italythere were two pro-Russian groups: NoName057(16) and Z-Pentest. Hackers have crashed the refrigeration systems of refrigerators. They exploited vulnerabilities in obsolete software, developed by the Danish multinational Danfoss, and in Dixell Xweb systems. It is only the latest wave of web offensives, the most striking, given that the researchers of Forescout they tracked more than 20 similar incidents claimed since January 2026 by the same hackers.
They also targeted three factories of Coolworld, the company that provides refrigeration services to the French national blood institute. The objective was the cold storage rooms that allow the conservation of blood and plasma bags useful for transfusions. Coolworld said that “the safety of the supplies was maintained thanks to the facilities’ monitoring and alarm systems”.
Electronic eyes for a few euros (even for thieves)
The enemies we find online can access any device that is not properly protected or not updated properly. If computer hackers have managed to bypass the security systems of institutions and companies, they can just as easily break into our homes by exploiting what we connect to the Wi-Fi network. And like computer pirates, thieves can also exploit technology to choose and monitor the apartments to burgle.
The most sensitive systems are the cameras we install in our homes. The intent can be noble and respond to a desire for security and control: supervise the apartment when you are on holiday, monitor your pet during working hours, check how your child is doing in the cot without getting out of bed. However, one must be aware of the risks that electronic eyes bring with them. Especially if you prefer the convenience of a device found on an online store or bought from unreliable neighborhood retailers to security.
Just browse the main e-commerce platforms to recognize the models installed in your neighbour’s, uncle’s or colleague’s house. They are cameras connected to Wi-Fi, with very high resolutions, subject tracking via Ai and even night vision. All for less than 20 euros. They are devices with Chinese systems, most of the time, and with blocked software and firmware updates. The cameras are of excellent quality: it is our home network which is often open to anyone.
The De Martino case: what the camera can hide
Two cases in national news show the danger of home video surveillance systems. In August 2025, the lawyers of Rai host Stefano De Martino filed a complaint relating to the images and videos circulated online depicting the showman with his then girlfriend Caroline Tronelli. One or more hackers would have managed to break into the system and steal videos of the two, which were then disseminated in chats and platforms.
I’ll tell you how hackers spy inside our homes – by Massimo Canorro
Just a month later, Yarix, an Italian center specializing in cybersecurity, discovered a dozen websites relaunching on their platforms thousands of videos stolen from home video cameras installed in private homes, medical practices and beauty centers. The portals allowed short extracts from the cameras to be viewed free of charge to encourage the purchase of the available packages. The services offered ranged from the possibility of accessing a specific camera to viewing the “content” with multiple clicks, usually with pornographic material without the knowledge of the protagonists. You could spend a few euros, but the most expensive plan involved spending 600 euros.
So Russian spies also exploit our homes
An overview of the situation was offered in July 2026 by Censys, a US company that maps devices accessible via the Internet. In a item takes up the concerns of the Dutch intelligence services (Aivd and Mivd) which denounced the digital espionage activities of Russian state agents through hacking of cameras connected to the Internet in Europe and in the NATO countries, as well as in Ukraine.
Censys explains that this is not surprising: “Conducting espionage activities through hacked cameras is nothing new.” Indeed, it has been reported several times that hackers can collect footage via IP (Internet protocol) cameras, i.e. those that transform images into digital format and send them directly to a local network (LAN) or to the Internet with an Ethernet or Wi-Fi cable.
| Village | Number of cameras | Number of cameras with a potentially exploitable vulnerability |
| Belgium | 24,659 | 1,168 |
| France | 68,317 | 8,977 |
| Germany | 65,539 | 8,401 |
| Greece | 24,623 | 649 |
| Italy | 99,203 | 12,678 |
| Portugal | 34,713 | 1,286 |
| Spain | 81,371 | 8,685 |
| Ukraine | 60,487 | 4,097 |
| United Kingdom | 113,962 | 7,142 |
Internet-connected cameras are constantly growing. The fact that they are accessible to the public does not automatically make them vulnerable to cyber attacks. In Italy there are 99,203 connected cameras, of which 12,678 with a potentially exploitable vulnerability. And the number could be even higher given that the Censys report does not include zero-day vulnerabilities (security flaws unknown to those who developed the system) nor devices with weak or compromised credentials.
Refrigerators, smart TVs and boilers: what is at risk
But the enemies in the house are not only hidden behind the electronic eyes that monitor the entrances to our apartment or the newborn in the crib. The Internet of things, the network made up of household appliances connected directly to the web or connected to each other, has multiplied the fronts from which to defend ourselves. Hackers, reports the Financial Timesthey can exploit home routers, smart refrigerators and all other devices to launch cyber attacks even against national infrastructures and institutions. The main European security agencies are aware of this risk and governments are trying to prevent possible flaws with more stringent regulations and recommendations to citizens.
This is how hackers and 007s see, read and listen to our lives – by Massimo Canorro
A report published on October 22, 2026 by Bitdefender, an antivirus software, and Netgear, a networking company, documents nine months of automated monitoring on approximately 10.4 million routers protected by Bitdefender. During this time, 5.4 billion security events and 6.2 billion vulnerability detections related to devices connected to routers were recorded.
Among the devices analyzed in the study are smart TVs. Some TVs, according to third-party investigations, may collect voice recordings, details about other devices connected to the local Wi-Fi network, geographic location and surrounding networks. In some cases, monitoring may continue even when the TV appears turned off or disconnected.
Another exposed nerve are the heating systems. On the market there are numerous models of smart boilers connected to the home Wi-Fi and manageable remotely. These devices can also be subject to attacks by attackers who have discovered a flaw in the local network or have managed to break into the application that manages consumption.
Furthermore, international news documents how hackers manage to infiltrate even large power plants that serve hundreds of thousands of customers. At the end of December 2025, a coordinated offensive hit a Polish cogeneration plant that serves almost half a million people. Luckily the detection software stopped the “wiper” malware in time. A year earlier, the FrostyGoop malware attack against the heating systems of Lviv (Ukraine) was successful, leaving over 600 buildings without hot water for two days.
Italian hospitals: billions of clinical data online
The level of the hacker attack can also be raised and the bad guys can attack ministries, banks, databases and even hospitals. The latter allow access to the most intimate sphere of a person and preserve precious information on patients, who can also be successful managers, entrepreneurs, VIPs and heads of state.
There are numerous cases of data exfiltrated from Italian healthcare facilities. In June 2024, Asst Rhodense, near Milan, was hit by ransomware by the cybercrime group Cicada3301 which published approximately 1 Terabyte of sensitive data online. Even earlier, in May ’23, the victim had been the ASL 1 Abruzzo from which the Monti hacker group had stolen 389 Gigabytes, which then ended up on the dark web.
Every device connected to the Internet can be the subject of a hacker attack, especially if it is old and not updated over time. The internet has simplified many aspects of our lives, but it has also allowed anyone with decent computer skills to enter our homes and steal our data, secrets and memories. Simply sitting at a desk, even on the other side of the world.
Dossier is the exclusive subscription investigative section of The Vermilion. If you want to support our journalistic work and subscribe, Click here.